Password Reset and Recovery Explained
A password reset is one of those processes nobody reads about until they need it urgently, usually at an inconvenient hour. It is worth understanding beforehand, because the design of the reset flow tells you a lot about how seriously a provider treats account security, and because knowing the steps removes most of the stress when it finally happens to you.
The central question is simple: how does the provider know it is you when you cannot prove it with a password? Every answer to that question has a weakness, and understanding where the weakness lies helps you strengthen the parts you control before you ever need to use them.
How a reset request is verified
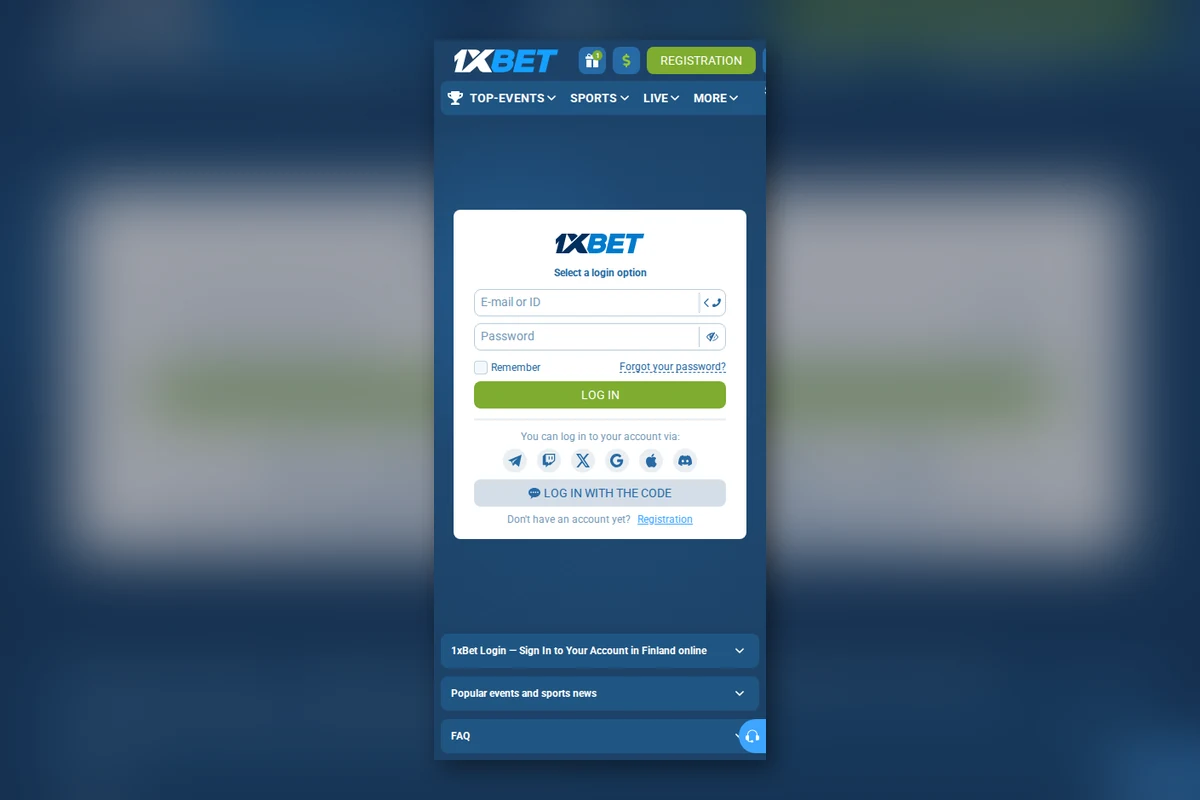
The reset flow begins with a request and continues with proof. You tell the system which account you want, and it sends a code or a link to a channel it already associates with you. The security of the whole process rests on that channel being under your control and nobody else having access to it at that moment.
Devices accumulate sessions. A phone replaced last year, a tablet in a drawer, a work laptop that has since been handed back - each may still hold an active session on your account. Reviewing and revoking those sessions periodically closes doors you had forgotten were open at all.
Email and phone recovery compared
Email is flexible and slow; a phone number is fast and tied to a physical object. Email can be read from anywhere, which helps when you are travelling and hurts when the mailbox itself is compromised. A phone number is harder to reach remotely, which is exactly why it is the more common choice for the second step.
Support conversations are a favourite target of fraud, because support staff are expected to be helpful. A genuine team never needs your full password, your card number or a code sent to your phone. Anyone who asks for those things is not helping you, however convincing their message looks.
- Keep the recovery email and phone number current.
- Treat security answers as passwords and store them safely.
- Prefer a long passphrase over a short scrambled string.
- Clear stored credentials before retyping after a lockout.
- Expect document checks if recovery reaches support.
Security questions and their weakness
Security questions have a deservedly poor reputation. The honest answers are often discoverable from public profiles, and the dishonest answers are forgettable. If a provider still uses them, treat the answers as another password: write something memorable to you and impossible for anyone else to guess from your history.
Session expiry is a feature rather than an annoyance. Being signed out after a period of inactivity limits the damage if a device is lost or borrowed, and it is worth understanding how long the provider allows before you decide to tick a box that keeps you signed in indefinitely.
Choosing a new password properly
A new password is an opportunity rather than a chore. Length matters more than punctuation, a phrase is easier to remember than a scramble, and uniqueness matters more than either. If the new password resembles the old one, or is reused from another service, the reset has achieved very little beyond a few minutes of inconvenience.
If an account is accessed by someone else, the first symptom is usually not a dramatic theft. It is a small change: a limit adjusted, a detail edited, a session that closed for no reason. Reviewing your account settings occasionally is how those quiet alterations get noticed while they are still small.
| Recovery channel | Strength | Main risk |
|---|---|---|
| Email link | Works anywhere, easy to use | Compromised mailbox |
| Phone code | Tied to a physical device | Lost or replaced handset |
| Support request | Possible when all else fails | Slow, and needs identification |
Avoiding repeated lockouts
Repeated lockouts usually have an unglamorous cause: an old password typed from memory, a keyboard set to the wrong layout, an autofill entry that was never updated. Clearing stored credentials and typing the password deliberately, once, is a better use of five minutes than ten rapid attempts that trigger further protective blocks.
Recovery details are the plan B of account security, and they are only useful if they are current. A phone number that has been recycled, an email address you no longer read or a security question with an answer anyone can guess will all fail at exactly the moment you need them most.
When recovery fails entirely
If recovery genuinely fails, the honest answer is that it becomes a support matter with a person at the other end. Expect to prove your identity with documents, expect it to take time, and expect the provider to be cautious. A provider that restores access instantly on request is not one to trust with an account that holds money.
There is no penalty for signing in less often. Nothing about a betting account requires daily attention, and an account opened deliberately rather than reflexively is more likely to be used within the limits you set. Convenience features should serve that habit rather than undermine it.
A reset flow is a security design in miniature, and the parts you control are the parts that matter most. Keep the recovery details current, choose a genuinely new password, and avoid the loop of hasty retries. Nothing about access changes what happens to a bet, and no setting can make an uncertain event certain. This material is informational and written for adults aged 18 and over who keep their play inside limits they have chosen.
Read next
Login: How Account Access Works
From the sign-in screen to a working session, and the parts of the process that matter.
Two-Step Verification for a Betting Account
What the second factor adds, where the codes come from and the usual mistakes.
Login Problems: A Troubleshooting Checklist
Wrong password, expired session, blocked device — work through it in a sensible order.